

Professional Certification
Become A Certified Data Protection Officer (CDPO)
Master global privacy regulations and secure organizational data. Advance your career in data protection with our industry-recognized certification program.
Global Recognition
The Certified Data Protection Officer (CDPO) course is accredited by the Institute of Information Management (IIM) Africa.
Professional Certification
Become A Certified Data Protection Officer (CDPO)
Master global privacy regulations and secure organizational data. Advance your career in data protection with our industry-recognized certification program.
Why Choose Our CDPO Certification Course?
Designed for modern privacy professionals, our curriculum ensures you are ready to tackle complex regulatory landscapes.
Expert-Led
Learn directly from seasoned Data Protection and Privacy Compliance professionals.
Flexible Learning
100% online modules designed to fit around your demanding professional schedule.
Comprehensive Curriculum
Covering the NDPA and other global privacy frameworks in depth.
Global Recognition
Accredited by The Institute of Information Management (IIM), Africa.
Expert-Led
Learn directly from seasoned Data Protection and Privacy Compliance professionals.
Flexible Learning
100% online modules designed to fit around your demanding professional schedule.
Comprehensive Curriculum
Covering the NDPA and other global privacy frameworks in depth.
Course Overview
A comprehensive training program combining theoretical knowledge with practical application.
Module 1: Introduction to Data Protection and Privacy
Establish a strong foundation in core privacy concepts. This module covers the history of data protection, key definitions, and the fundamental principles that govern modern privacy laws.
Key Learning Outcomes
- Understand the evolution of privacy rights.
- Differentiate between personal data types.
- Grasp core principles (e.g., minimization, purpose limitation).
- Identify key stakeholders in data processing.
Module 2: Principles and Lawful Bases for Data Processing
Dive into the operational core of compliance. This module explores the mandatory principles guiding data activities and how to establish a valid, lawful justification for processing.
Key Learning Outcomes
Evaluate data activities against core processing principles.
Apply purpose limitation and data minimization in practice.
Understand the duty of care, security, and accountability.
- Determine the appropriate lawful basis under the NDP Act 2023.
Module 3: Rights of Data Subjects
Shift focus to the individuals whose data you collect. This module breaks down the specific legal rights guaranteed to data subjects and your organization’s obligations to fulfill them.
Key Learning Outcomes
Identify valid data subjects and their fundamental rights.
Manage requests for access, rectification, and erasure.
Handle objections, processing restrictions, and automated profiling.
Operationalize Data Subject Rights (DSR) workflows efficiently.
Module 4: Obligations of Data Controllers/ Processors
Dissect the vital roles within the data protection ecosystem. This module outlines the legal distinctions and strict operational duties of those who control and process personal data.
Key Learning Outcomes
Differentiate the roles of Data Controllers and Data Processors.
Map the shared and specific responsibilities of each entity.
Implement mandatory compliance obligations under the NDP Act.
Recognize the regulatory and financial consequences of non-compliance.
Module 5: Data Security
Transition into the technical and procedural defenses required to safeguard information. This module covers proactive security measures and reactive incident management protocols.
Key Learning Outcomes
Distinguish between security incidents and actual data breaches.
Implement technical and organizational protective measures.
Execute incident response and 72-hour breach notification protocols.
Apply de-identification techniques like pseudonymization and anonymization.
Module 6: Managing Third-Party Risk: Vendors, Partners and Collaborations
Address the vulnerabilities introduced when sharing data externally. This module provides a framework for assessing and mitigating risks associated with third-party vendors and partners.
Key Learning Outcomes
Categorize data-related risks introduced by third parties.
Conduct comprehensive risk assessment and evaluation techniques.
Navigate the complete third-party vendor due diligence lifecycle.
Enforce controller and processor due diligence obligations.
Module 7: Cross-Border Data Transfers
Tackle the complexities of moving personal information internationally. This module covers the legal mechanisms and safeguards required to transfer data outside its original jurisdiction compliantly.
Key Learning Outcomes
Grasp the legal concept of cross-border data flows.
Evaluate the requirements for adequacy decisions.
Implement core transfer instruments and fallback mechanisms.
Safeguard personal data against international jurisdictional challenges.
Module 8: Emerging Technologies and Data Protection
Examine the intersection of rapid technological advancement and privacy frameworks. This module explores how to apply regulatory principles to innovations like AI and big data.
Key Learning Outcomes
Understand the privacy challenges posed by emerging technologies.
Identify vulnerabilities introduced by automated systems and algorithms.
Align the adoption of new tools with the NDP Act provisions.
Integrate privacy by design into future technology deployments.
Module 9: Roles and Responsibilities of a Data Protection Officer
Focus on the pivotal role at the center of organizational compliance. This module defines the DPO’s authority, independence, and day-to-day duties in championing privacy.
Key Learning Outcomes
Define the independence and regulatory standing of the DPO.
Enforce core data protection principles internally.
Ensure organizational accountability, accuracy, and security.
Facilitate regulatory audits and act as the primary NDPC liaison.
Appendix 1: DSAR Third-Party Requests, ROPA, and Incident Response
Focus on the pivotal role at the center of organizational compliance. This module defines the DPO’s authority, independence, and day-to-day duties in championing privacy.
Key Learning Outcomes
Define the independence and regulatory standing of the DPO.
Enforce core data protection principles internally.
Ensure organizational accountability, accuracy, and security.
Facilitate regulatory audits and act as the primary NDPC liaison.
Appendix II: Convention 108+, GDPR, AUCC, ECOWAS & NDPA GAID
Broaden your scope from national regulations to global and regional frameworks. This final section explores the international treaties and directives shaping cross-border data privacy.
Key Learning Outcomes
Understand global baseline standards via Convention 108+ and GDPR.
Analyze the African Union (AUCC) and ECOWAS regional frameworks.
Operationalize the NDPC’s General Application and Implementation Directive (GAID).
Navigate international compliance and tiered data controller registrations.
Course Curriculum
Module 1: Introduction to Data Protection and Privacy
Establish a strong foundation in core privacy concepts. This module covers the history of data protection, key definitions, and the fundamental principles that govern modern privacy laws.
Key Learning Outcomes
- Understand the evolution of privacy rights.
- Differentiate between personal data types.
- Grasp core principles (e.g., minimization, purpose limitation).
- Identify key stakeholders in data processing.
Module 2: Principles and Lawful Bases for Data Processing
Dive into the operational core of compliance. This module explores the mandatory principles guiding data activities and how to establish a valid, lawful justification for processing.
Key Learning Outcomes
Evaluate data activities against core processing principles.
Apply purpose limitation and data minimization in practice.
Understand the duty of care, security, and accountability.
- Determine the appropriate lawful basis under the NDP Act 2023.
Module 3: Rights of Data Subjects
Shift focus to the individuals whose data you collect. This module breaks down the specific legal rights guaranteed to data subjects and your organization’s obligations to fulfill them.
Key Learning Outcomes
Identify valid data subjects and their fundamental rights.
Manage requests for access, rectification, and erasure.
Handle objections, processing restrictions, and automated profiling.
Operationalize Data Subject Rights (DSR) workflows efficiently.
Module 4: Obligations of Data Controllers/ Processors
Dissect the vital roles within the data protection ecosystem. This module outlines the legal distinctions and strict operational duties of those who control and process personal data.
Key Learning Outcomes
Differentiate the roles of Data Controllers and Data Processors.
Map the shared and specific responsibilities of each entity.
Implement mandatory compliance obligations under the NDP Act.
Recognize the regulatory and financial consequences of non-compliance.
Module 5: Data Security
Transition into the technical and procedural defenses required to safeguard information. This module covers proactive security measures and reactive incident management protocols.
Key Learning Outcomes
Distinguish between security incidents and actual data breaches.
Implement technical and organizational protective measures.
Execute incident response and 72-hour breach notification protocols.
Apply de-identification techniques like pseudonymization and anonymization.
Module 6: Managing Third-Party Risk: Vendors, Partners and Collaborations
Address the vulnerabilities introduced when sharing data externally. This module provides a framework for assessing and mitigating risks associated with third-party vendors and partners.
Key Learning Outcomes
Categorize data-related risks introduced by third parties.
Conduct comprehensive risk assessment and evaluation techniques.
Navigate the complete third-party vendor due diligence lifecycle.
Enforce controller and processor due diligence obligations.
Module 7: Cross-Border Data Transfers
Tackle the complexities of moving personal information internationally. This module covers the legal mechanisms and safeguards required to transfer data outside its original jurisdiction compliantly.
Key Learning Outcomes
Grasp the legal concept of cross-border data flows.
Evaluate the requirements for adequacy decisions.
Implement core transfer instruments and fallback mechanisms.
Safeguard personal data against international jurisdictional challenges.
Module 8: Emerging Technologies and Data Protection
Examine the intersection of rapid technological advancement and privacy frameworks. This module explores how to apply regulatory principles to innovations like AI and big data.
Key Learning Outcomes
Understand the privacy challenges posed by emerging technologies.
Identify vulnerabilities introduced by automated systems and algorithms.
Align the adoption of new tools with the NDP Act provisions.
Integrate privacy by design into future technology deployments.
Module 9: Roles and Responsibilities of a Data Protection Officer
Focus on the pivotal role at the center of organizational compliance. This module defines the DPO’s authority, independence, and day-to-day duties in championing privacy.
Key Learning Outcomes
Define the independence and regulatory standing of the DPO.
Enforce core data protection principles internally.
Ensure organizational accountability, accuracy, and security.
Facilitate regulatory audits and act as the primary NDPC liaison.
Appendix 1: DSAR Third-Party Requests, ROPA, and Incident Response
Focus on the pivotal role at the center of organizational compliance. This module defines the DPO’s authority, independence, and day-to-day duties in championing privacy.
Key Learning Outcomes
Define the independence and regulatory standing of the DPO.
Enforce core data protection principles internally.
Ensure organizational accountability, accuracy, and security.
Facilitate regulatory audits and act as the primary NDPC liaison.
Appendix II: Convention 108+, GDPR, AUCC, ECOWAS & NDPA GAID
Broaden your scope from national regulations to global and regional frameworks. This final section explores the international treaties and directives shaping cross-border data privacy.
Key Learning Outcomes
Understand global baseline standards via Convention 108+ and GDPR.
Analyze the African Union (AUCC) and ECOWAS regional frameworks.
Operationalize the NDPC’s General Application and Implementation Directive (GAID).
Navigate international compliance and tiered data controller registrations.
Meet Your Instructor
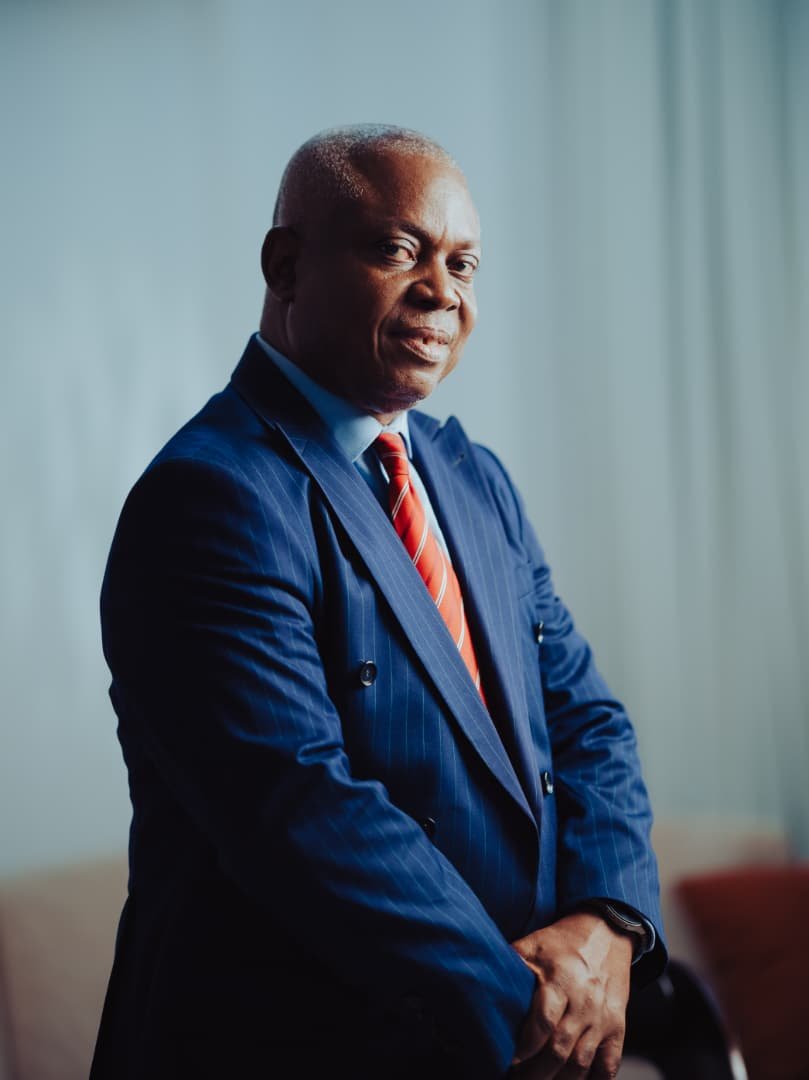
Dr. Wence Nwoga
FCIB, FCA, CISA, CISM, CGEIT, Ph.D
Dr. Wence Nwoga is a Compliance Consultant at DataPro Limited. He is highly knowledgeable in regulatory compliance and has served as a facilitator at numerous seminars and conferences on Data Protection and Privacy Compliance, as well as Governance, Cybersecurity Risk, and Compliance.
Lead Instructor
Dr. Wence Nwoga
FCIB, FCA, CISA, CISM, CGEIT, Ph.D
Dr. Wence Nwoga is a Compliance Consultant at DataPro Limited. He is highly knowledgeable in regulatory compliance and has served as a facilitator at numerous seminars and conferences on Data Protection and Privacy Compliance, as well as Governance, Cybersecurity Risk, and Compliance.
Ready to Advance Your Career?
Join the next cohort of data protection leaders. Enrollment closes soon for the upcoming term.